collana advises medium-sized businesses in the DACH region on IT security: assessing compliance and conducting gap analyses for NIS2, securing Microsoft environments with Entra ID and Defender, implementing access control policies in ERP systems, and providing ongoing operational monitoring. As a Microsoft Solutions Partner for Security, we work with the built-in tools that you have already licensed.
As we are already familiar with your ERP and data landscape, we implement security measures right where your business processes actually take place.
 Microsoft
 Microsoft
 Microsoft
 ERP-
The NIS2 Implementation Act has been in force in Germany since 6 December 2025, with no transition period. The group of companies subject to this requirement is grown from around 4,500 to approximately 29,500. The management bears personal liability.
Two questions, asked one after the other, will determine whether you are affected: Does your business fall within one of the categories of establishment listed in the Act? And do you exceed the size thresholds?
01


What matters is not the sector name, but the specific type of establishment described in the Act for each line. ‘Food’, for example, covers only wholesale trade and industrial production and processing. The manufacturing sector is defined by NACE divisions; waste management is only included if it is the main economic activity. Furthermore, a company may fall under several categories at the same time, for example as a manufacturer and, at the same time, as the operator of an energy storage facility.
02
| Particularly important facilities | Key facilities | |
|---|---|---|
| Sectors | Appendix 1 only | Appendix 1 and Appendix 2 |
| Size | 250 or more employees, or an annual turnover in excess of 50 million euros and, at the same time, total assets in excess of 43 million euros | 50 or more employees, or an annual turnover and balance sheet total each exceeding 10 million euros |
| Supervision | comprehensive, proactive supervision by the BSI pursuant to Section 61 of the BSIG | Ad hoc supervision pursuant to Section 62 of the BSIG |
| Fines | up to 10 million euros | up to 7 million euros |
Source: Section 28 of the BSIG for the scope of application, Section 65 of the BSIG for the levels of fines; Sections 61 and 62 of the BSIG for supervision. As at 18 September 2026.
In summary: A particularly important organisation is a company operating in a sector listed in Annex 1 with at least 250 employees or over 50 million euros in annual turnover with total assets exceeding 43 million euros. A major institution is an undertaking listed in Annex 1 or Annex 2 with at least 50 employees or annual turnover and balance sheet total of, in each case, over 10 million euros. Any organisation that falls within Annex 1 but only meets the lower thresholds is considered a key institution. A hospital with 80 staff members would therefore be classified in the second column, not the first.
Our IT security assessment shows you where action is needed and which measures make the most sense for your business as a priority.
We will bring you to a point, both technically and organisationally, where the formal implementation is just a manageable step away.
01
02
03
Registration with the BSI, the reporting deadlines for security incidents, the obligation to provide evidence to the supervisory authority, and the training requirement for senior management in accordance with Section 38 of the BSIG These are legal steps that you can take either on your own or with legal assistance. We ensure that nothing is overlooked in these steps that needs to be prepared from a technical or organisational perspective.
Before any investment is made, the current situation must be clearly laid out.
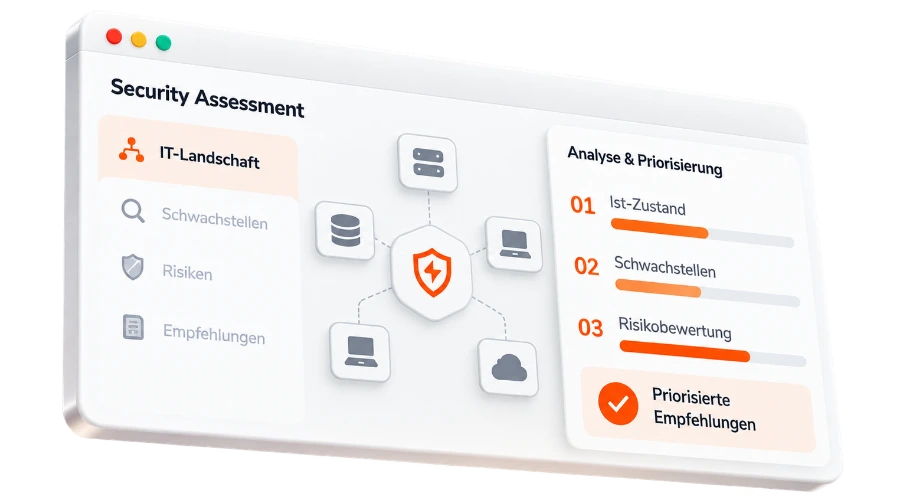
We analyse your IT environment for vulnerabilities and provide specific, prioritised recommendations for securing it. Not just a list of tools, but a sequence of steps tailored to your risk profile and budget.
We analyse your IT environment for vulnerabilities and provide specific, prioritised recommendations for securing it. Not just a list of tools, but a sequence of steps tailored to your risk profile and budget.
04
Our IT security assessment shows you where action is needed and which measures make the most sense for your business as a priority.

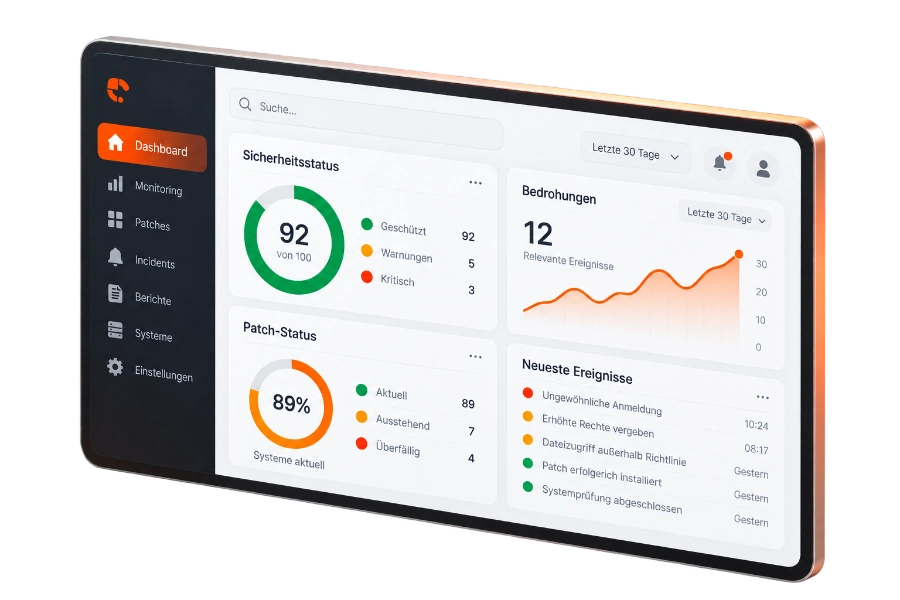
If required, this can form part of our Managed Services, meaning that system operation and security are all handled by a single provider, and nobody will pass the buck to another service provider in the event of an emergency.
We support you in complying with GDPR, ISO 27001 and industry-specific security standards.
Within the collana Group, Develappers GmbH is certified to ISO 27001. We therefore know from our own experience what is involved in setting up an ISMS, documenting it and undergoing an audit; our knowledge is not limited to a consultancy perspective.
The benefit for you is that the areas of action set out in Section 30 of the BSIG – in other words, the core of the NIS2 obligations – largely correspond to the requirements of ISO 27001. Anyone setting up an information security management system in accordance with ISO 27001 is, at the same time, working towards NIS2 compliance. Duplication of effort can be avoided if both are considered together from the outset.
Most successful attacks do not start with a technical vulnerability, but with an email that looks convincing enough. Training and awareness campaigns turn your staff into the strongest link in the security chain, rather than the weakest.
For management teams, there is a further requirement: the BSIG requires the governing bodies of the organisations concerned not only to monitor the implementation of security measures, but also to undergo regular training themselves.
Our IT security assessment shows you where action is needed and which measures make the most sense for your business as a priority.
This is determined in two steps. Firstly: Does any of your business activities fall under one of the types of organisation listed in Annex 1 or Annex 2 of the BSIG? Secondly: Do you meet the size thresholds, i.e. at least 50 employees, or an annual turnover and balance sheet total of more than 10 million euros each? Only when both criteria are met are you subject to the Act. The scope of application currently covers around 29,500 companies in Germany, many of which operate in the manufacturing sector, logistics, retail and the healthcare sector.
Yes, provided the size thresholds are met. Mechanical engineering is listed in Annex 2 of the BSIG under the manufacturing sector, defined by NACE Division 28. The same applies to the manufacture of motor vehicles and motor vehicle parts, other vehicle construction, electrical equipment, and data processing equipment and electronic products. Enterprises listed in Annex 2 are important facilities, not particularly important ones.
It is not automatic, but it goes a long way. The areas of action set out in Section 30 of the BSIG largely correspond to the ISO 27001 requirements. In addition, particular attention should be paid to registration with the BSI, the obligations to report security incidents, and the duties of senior management.
Whether it’s NIS2, Microsoft Security or authorisation models in ERP: let’s take a look at your current situation together and work out which measures make sense for your business. We’ll discuss the next steps in a no-obligation initial consultation.